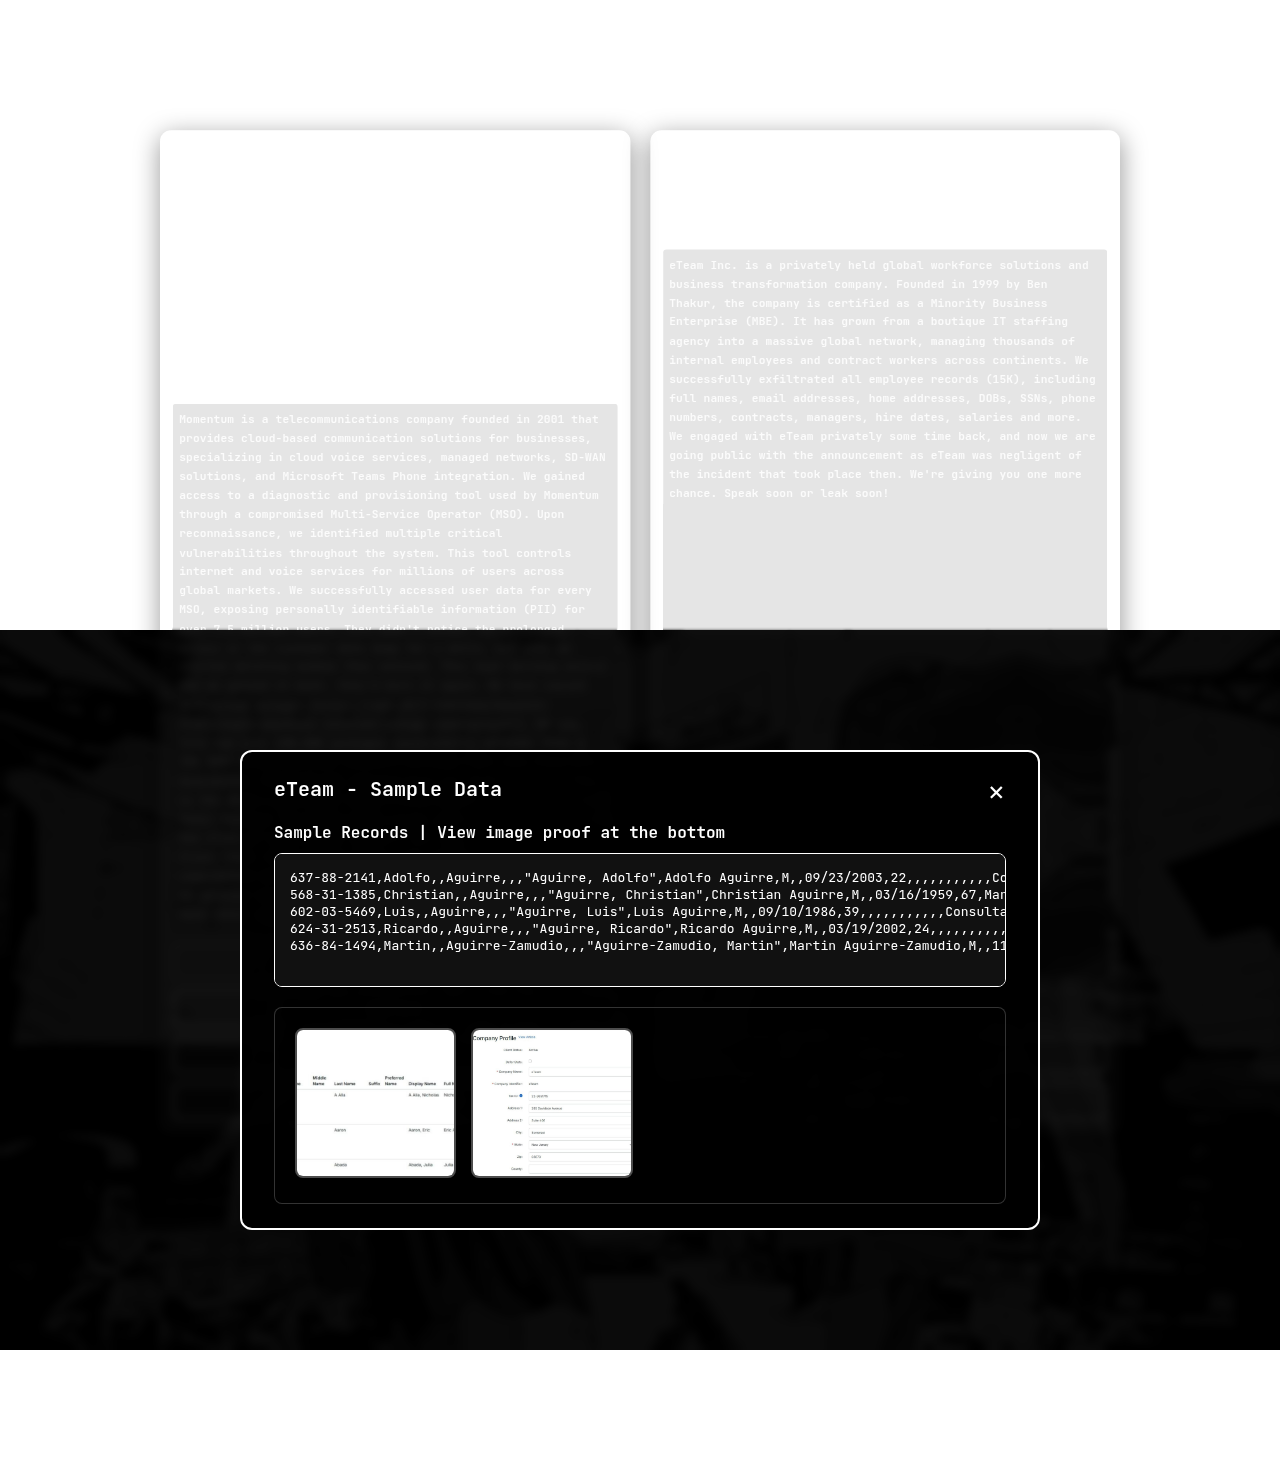
eTeam Inc. is a privately held global workforce solutions and business transformation company. Founded in 1999 by Ben Thakur, the company is certified as a Minority Business Enterprise (MBE). It has grown from a boutique IT staffing agency into a massive global network, managing thousands of internal employees and contract workers across continents. We successfully exfiltrated all employee records (15K), including full names, email addresses, home addresses, DOBs, SSNs, phone numbers, contracts, managers, hire dates, salaries and more. We engaged with eTeam privately some time back, and now we are going public with the announcement as eTeam was negligent of the incident that took place then. We're giving you one more chance. Speak soon or leak soon!
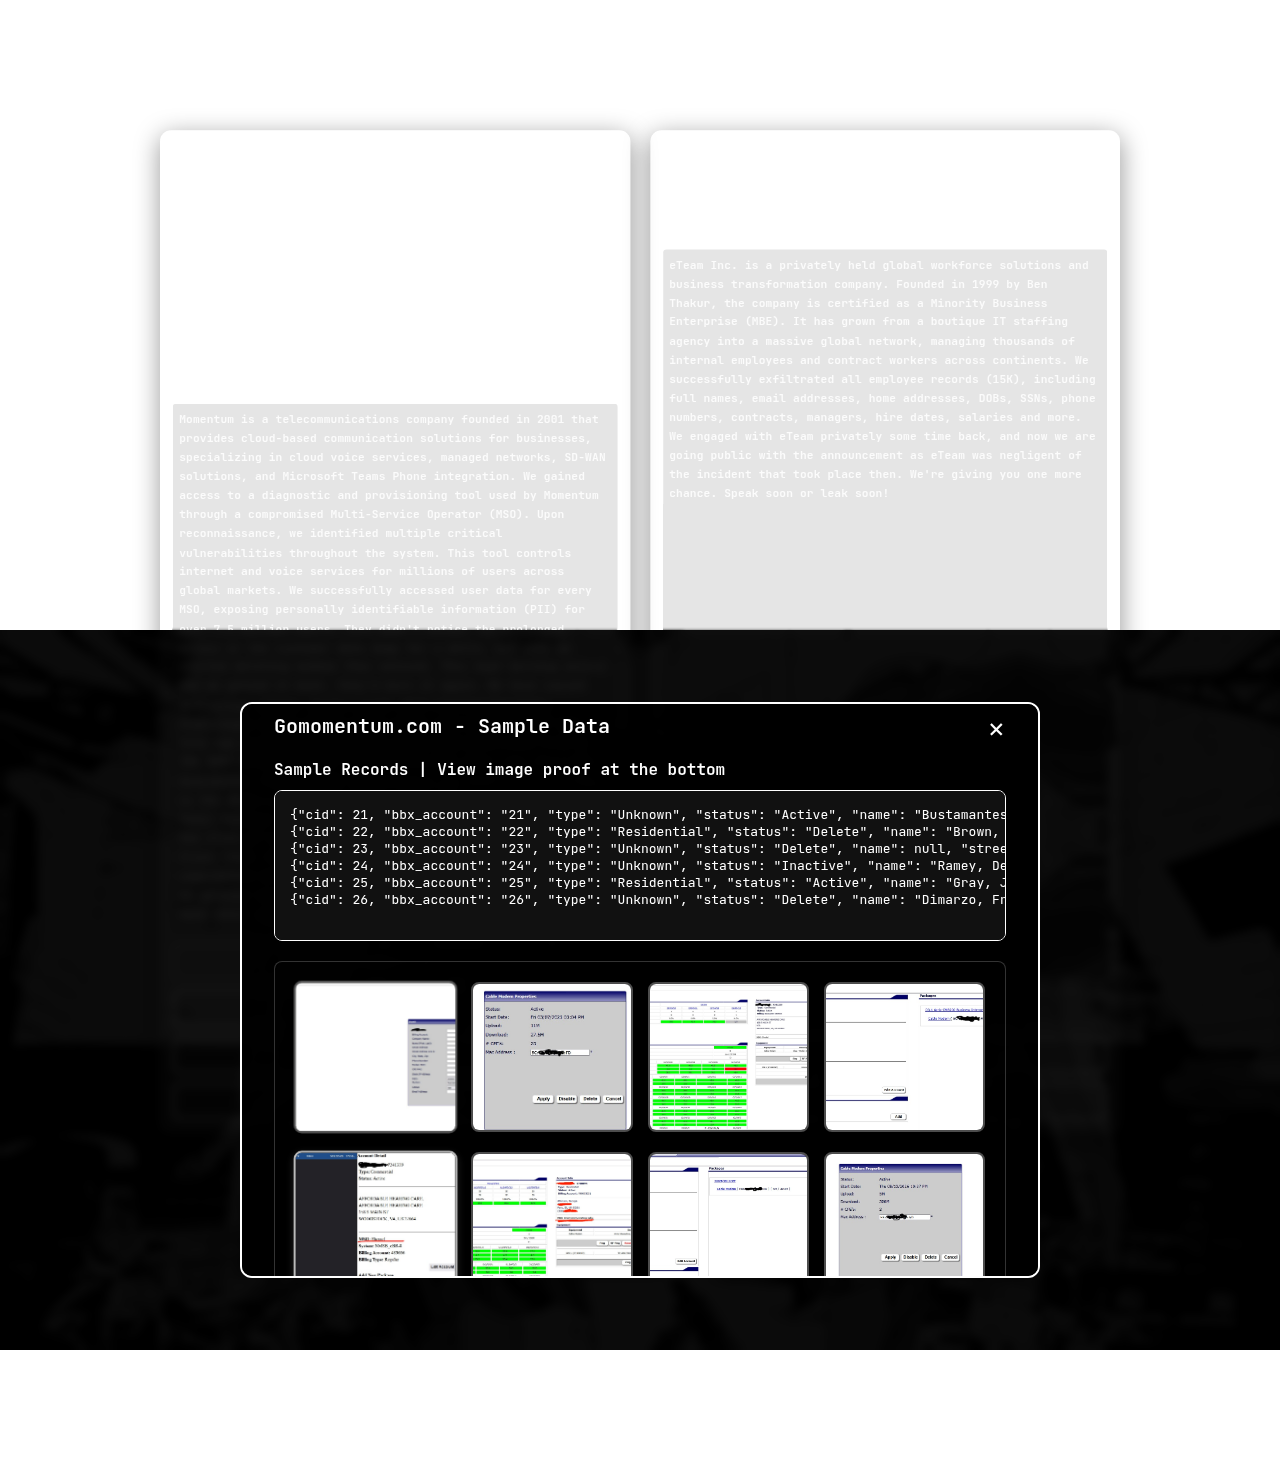
Gomomentum.com
Momentum is a telecommunications company founded in 2001 that provides cloud-based communication solutions for businesses, specializing in cloud voice services, managed networks, SD-WAN solutions, and Microsoft Teams Phone integration. We gained access to a diagnostic and provisioning tool used by Momentum through a compromised Multi-Service Operator (MSO). Upon reconnaissance, we identified multiple critical vulnerabilities throughout the system. This tool controls internet and voice services for millions of users across global markets. We successfully accessed user data for every MSO, exposing personally identifiable information (PII) for over 7.5 million users. They didn't notice the prolonged access or the customer data dump for a while, but when we started deleting modems they noticed. They kept burning access and we gained it back, they'd burn it again. We have caused widespread outages (https://www.abc4.com/news/wasatch-front/eagle-mountain-internet-outage-cyberattack/). We now have had over 100,000 packages successfully deleted. That's 100,000+ people without internet service right now. Families, businesses, students all cut off from the digital world. This is the direct result of their negligence and failure to secure their systems. These services can be restored immediately with the click of a button on our tool but you must reach out. Click "View Affected MSOs" below to see the full list of compromised providers. Momentum management should contact us to discuss resolution. Affected MSOs can also contact us to have their users' data deleted from our database.
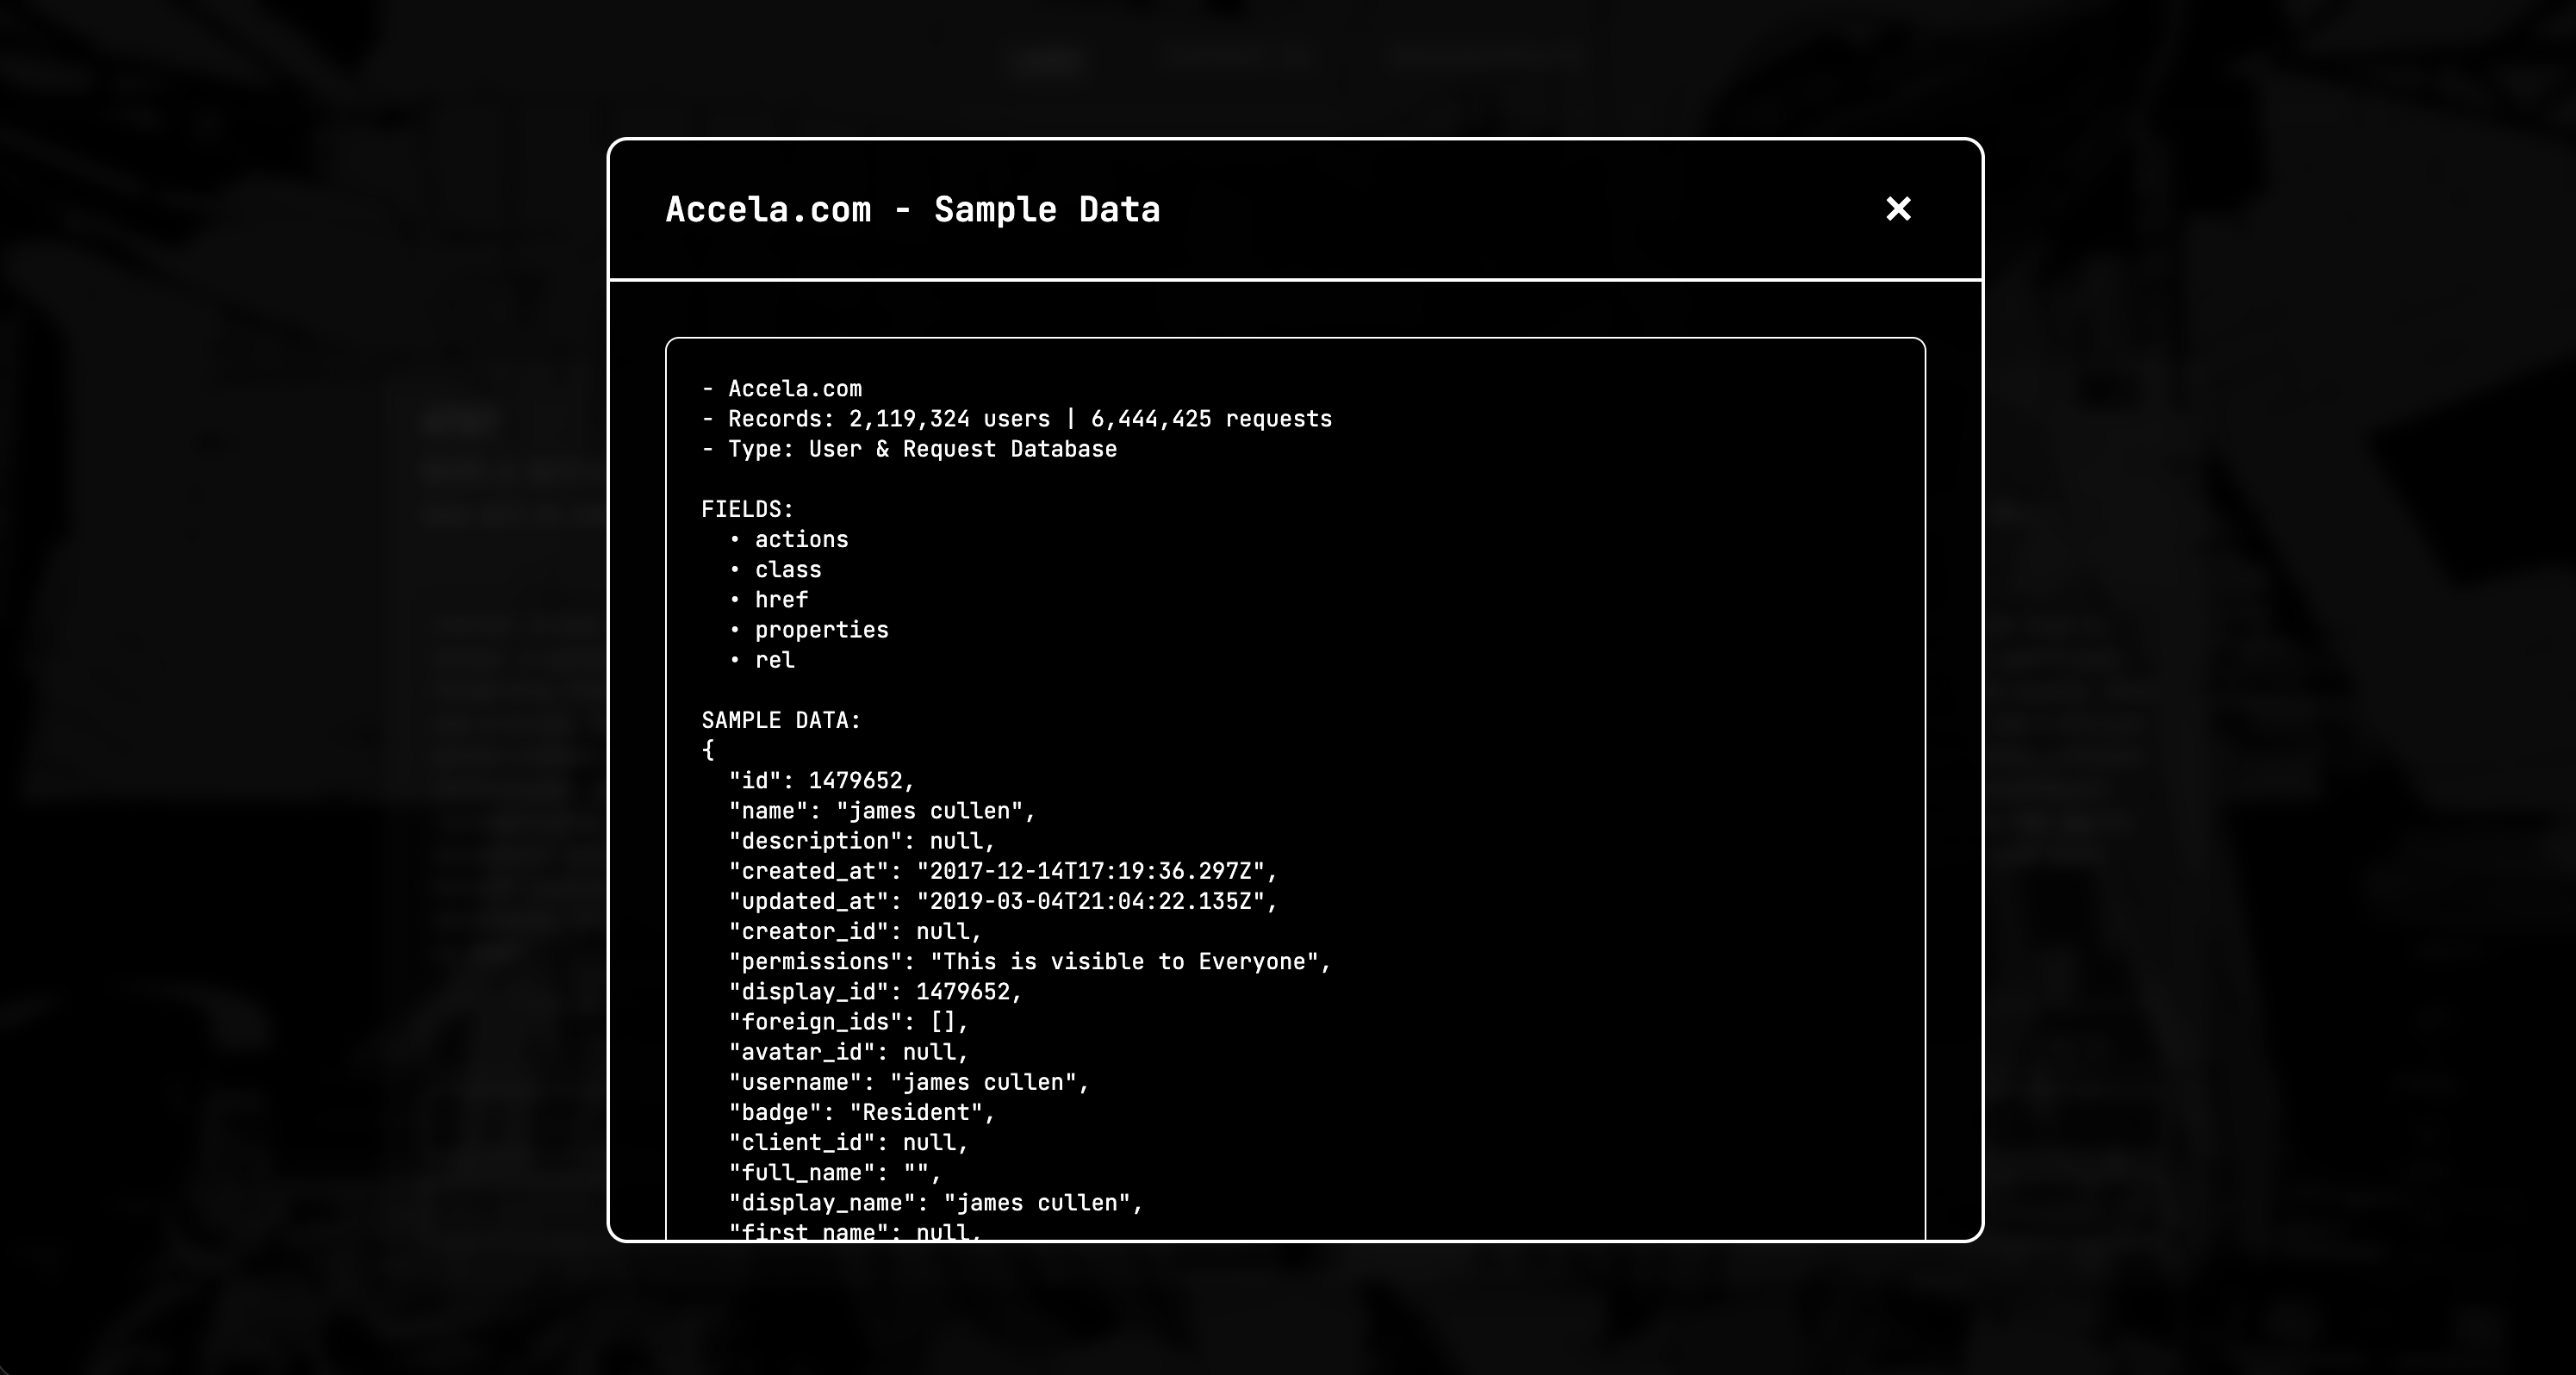
Accela.com
Accela is a comprehensive cloud based software platform used by state and local governments to manage internal agency operations. We have successfully extracted over 50 GB of data from Accela. Data includes over 2 million lines of user data with PII, and 6 million user requests (from their citizen engagement portal where citizens report everyday non-emergencies in/around their neighbourhoods) also with PII. There is a lot of government data, from FBI agents to cops to regular government workers. Speak soon or Leak soon!
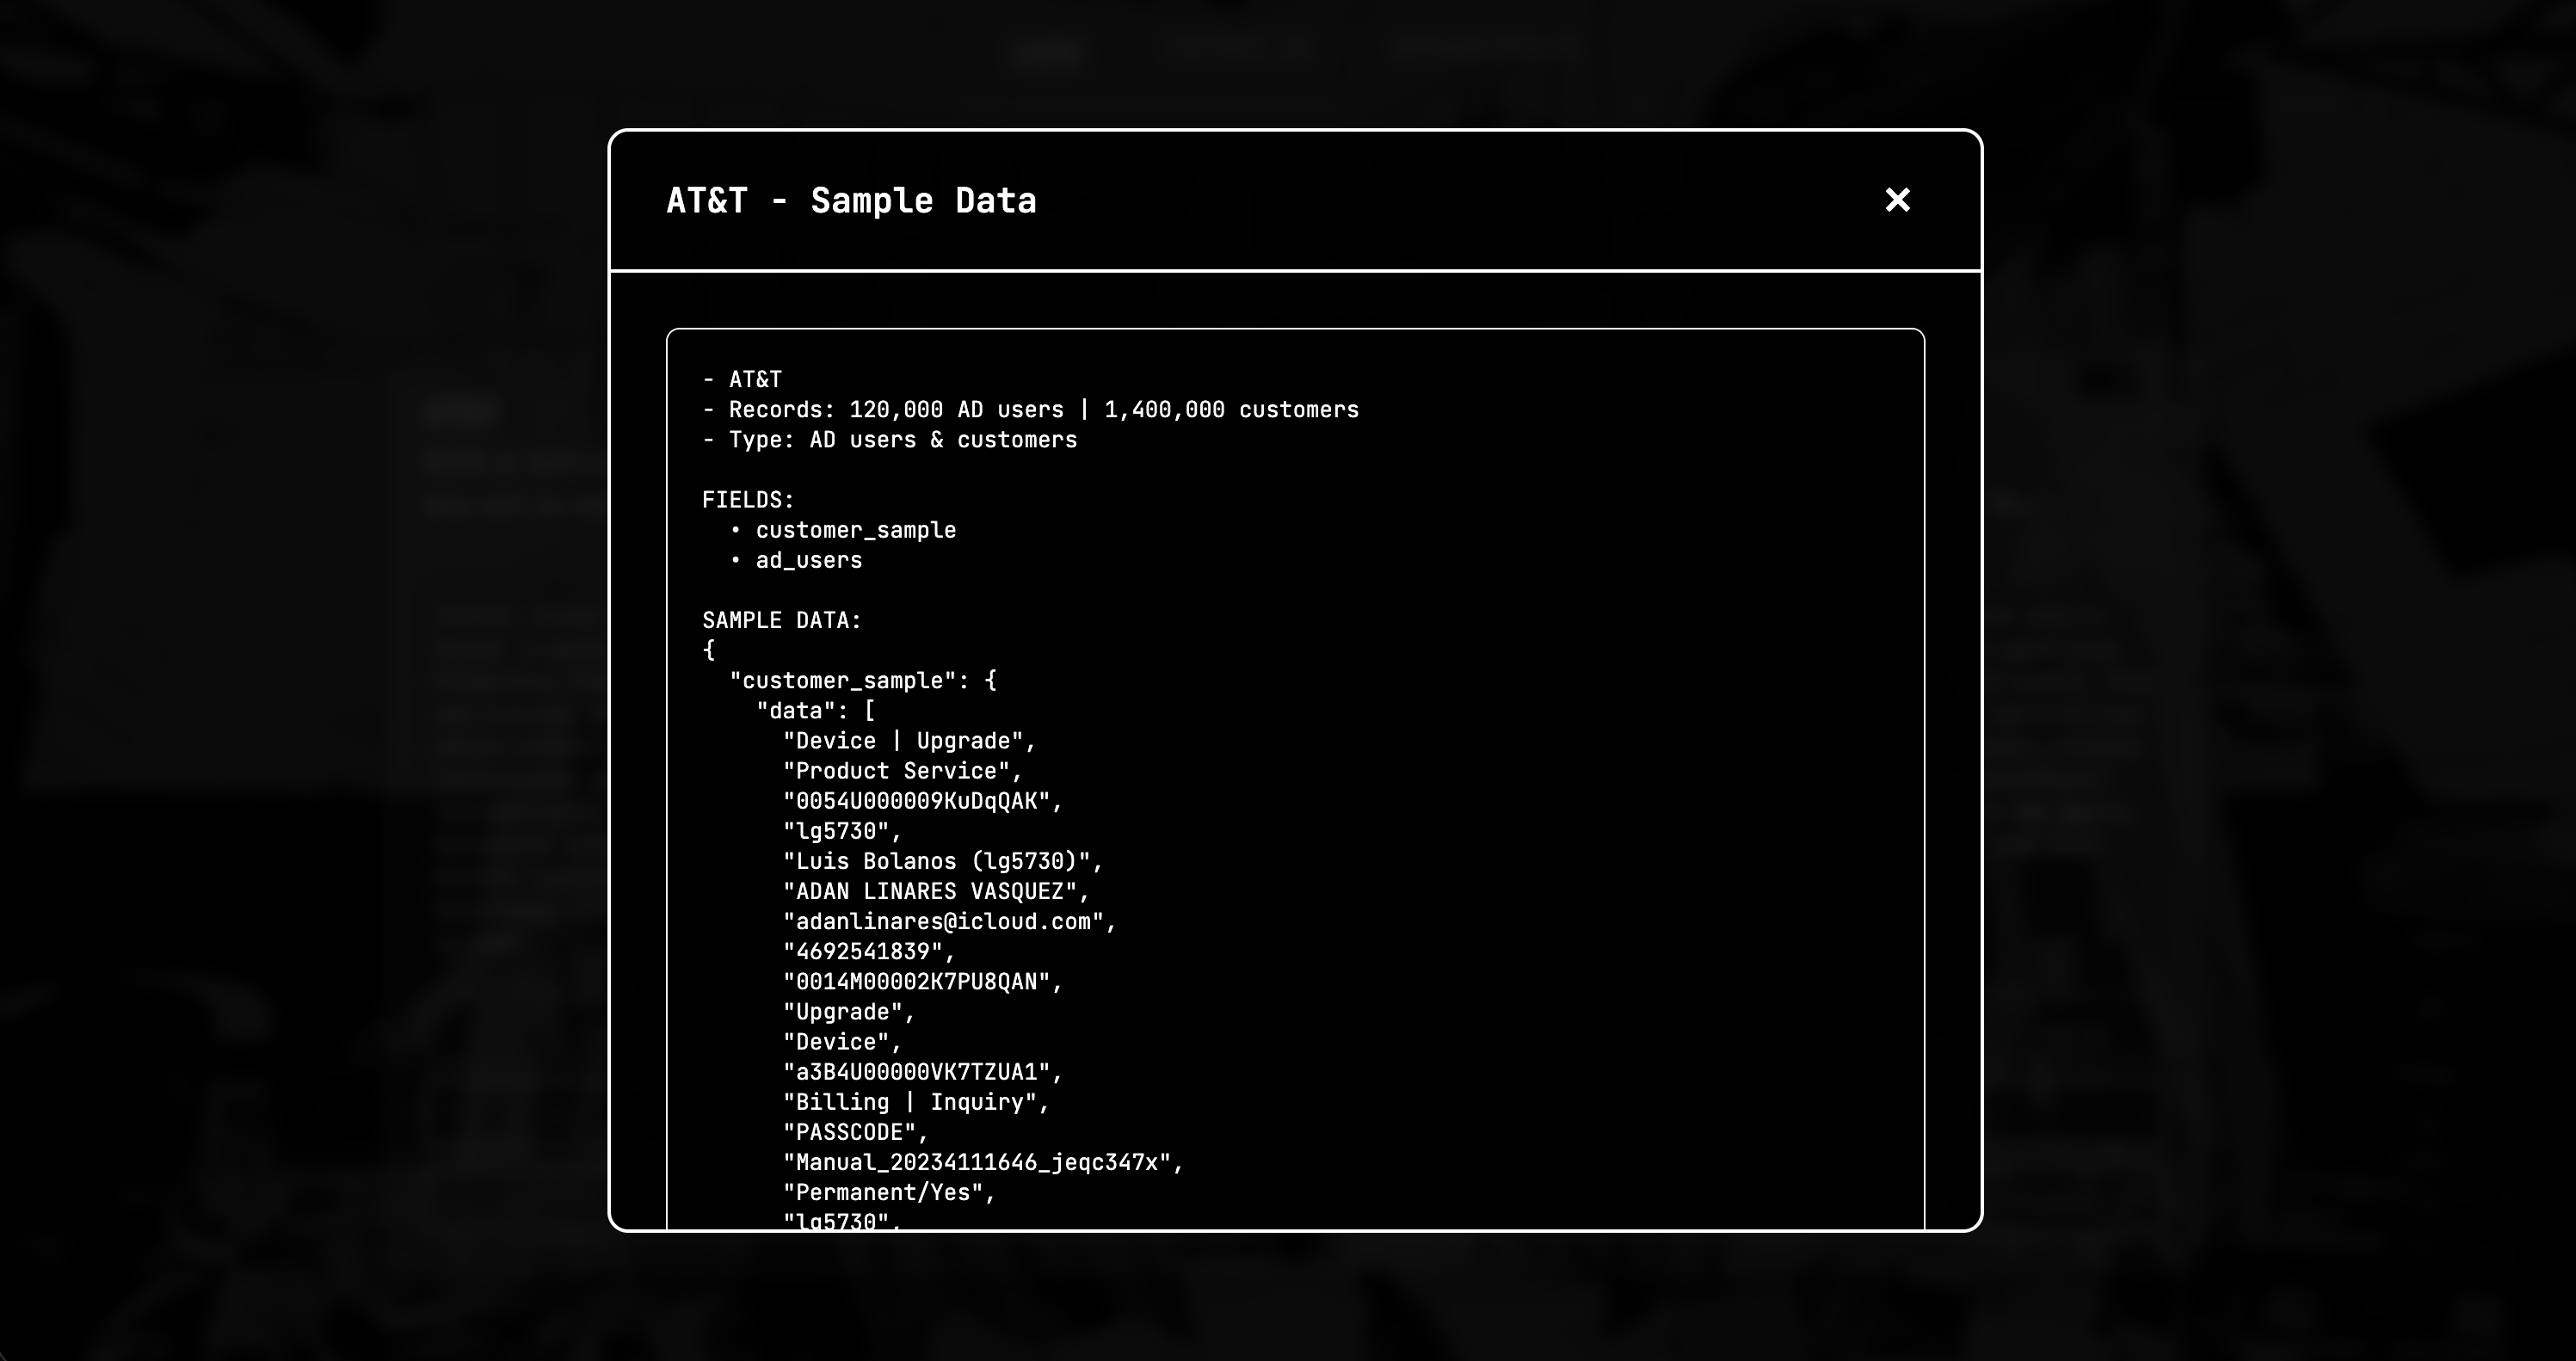
AT&T
Initial access was via a CX contractor doing business with AT&T. Access originally used as vehicle for Equipment Changes/Call Forwarding (thanks a lot TORCH patch) - VPN + HVD (both external and internal MyDesktop) instances were accessed for a prolonged period without any detection or incident response taking place. Certificates exported from certlm in the VDI + OPUS self installer (automatically joins EP to S1) opened up the door to the VPN. Salesforce data was accessed via a project manager ATTUID + a DirecTV contractor who for some reason had the apps available in Salesforce. AT&T CSO, if you are reading this, you are to contact us ASAP!