Company: PT Karya Teknik Utama (KTU Shipyard)
Location: Batam, Indonesia
Founded: 1982
Industry: Shipbuilding & Marine Engineering
Website: https://ktushipyard.com/
What the company does
KTU Shipyard is an Indonesian shipbuilding company specializing in the construction, repair and maintenance of commercial vessels.
Its main products and services include:
- Tugboats
- Barges
- Tankers and cargo vessels
- Crane barges
- Ship repair and maintenance
Company size
- Privately owned company.
- Approximately 501–1,000 employees.
- Multiple shipyard facilities in Indonesia.
- Claims to have built approximately 2,200 vessels.
Annual Revenue
~USD 200 million
Key Business Information
- Business model: B2B shipbuilding and marine services.
- Customers: Shipping companies, marine logistics operators and offshore businesses.
- Main market: Indonesia and regional maritime markets.
- Competitive advantage: Established shipbuilding experience, multiple facilities and diverse vessel manufacturing capabilities.
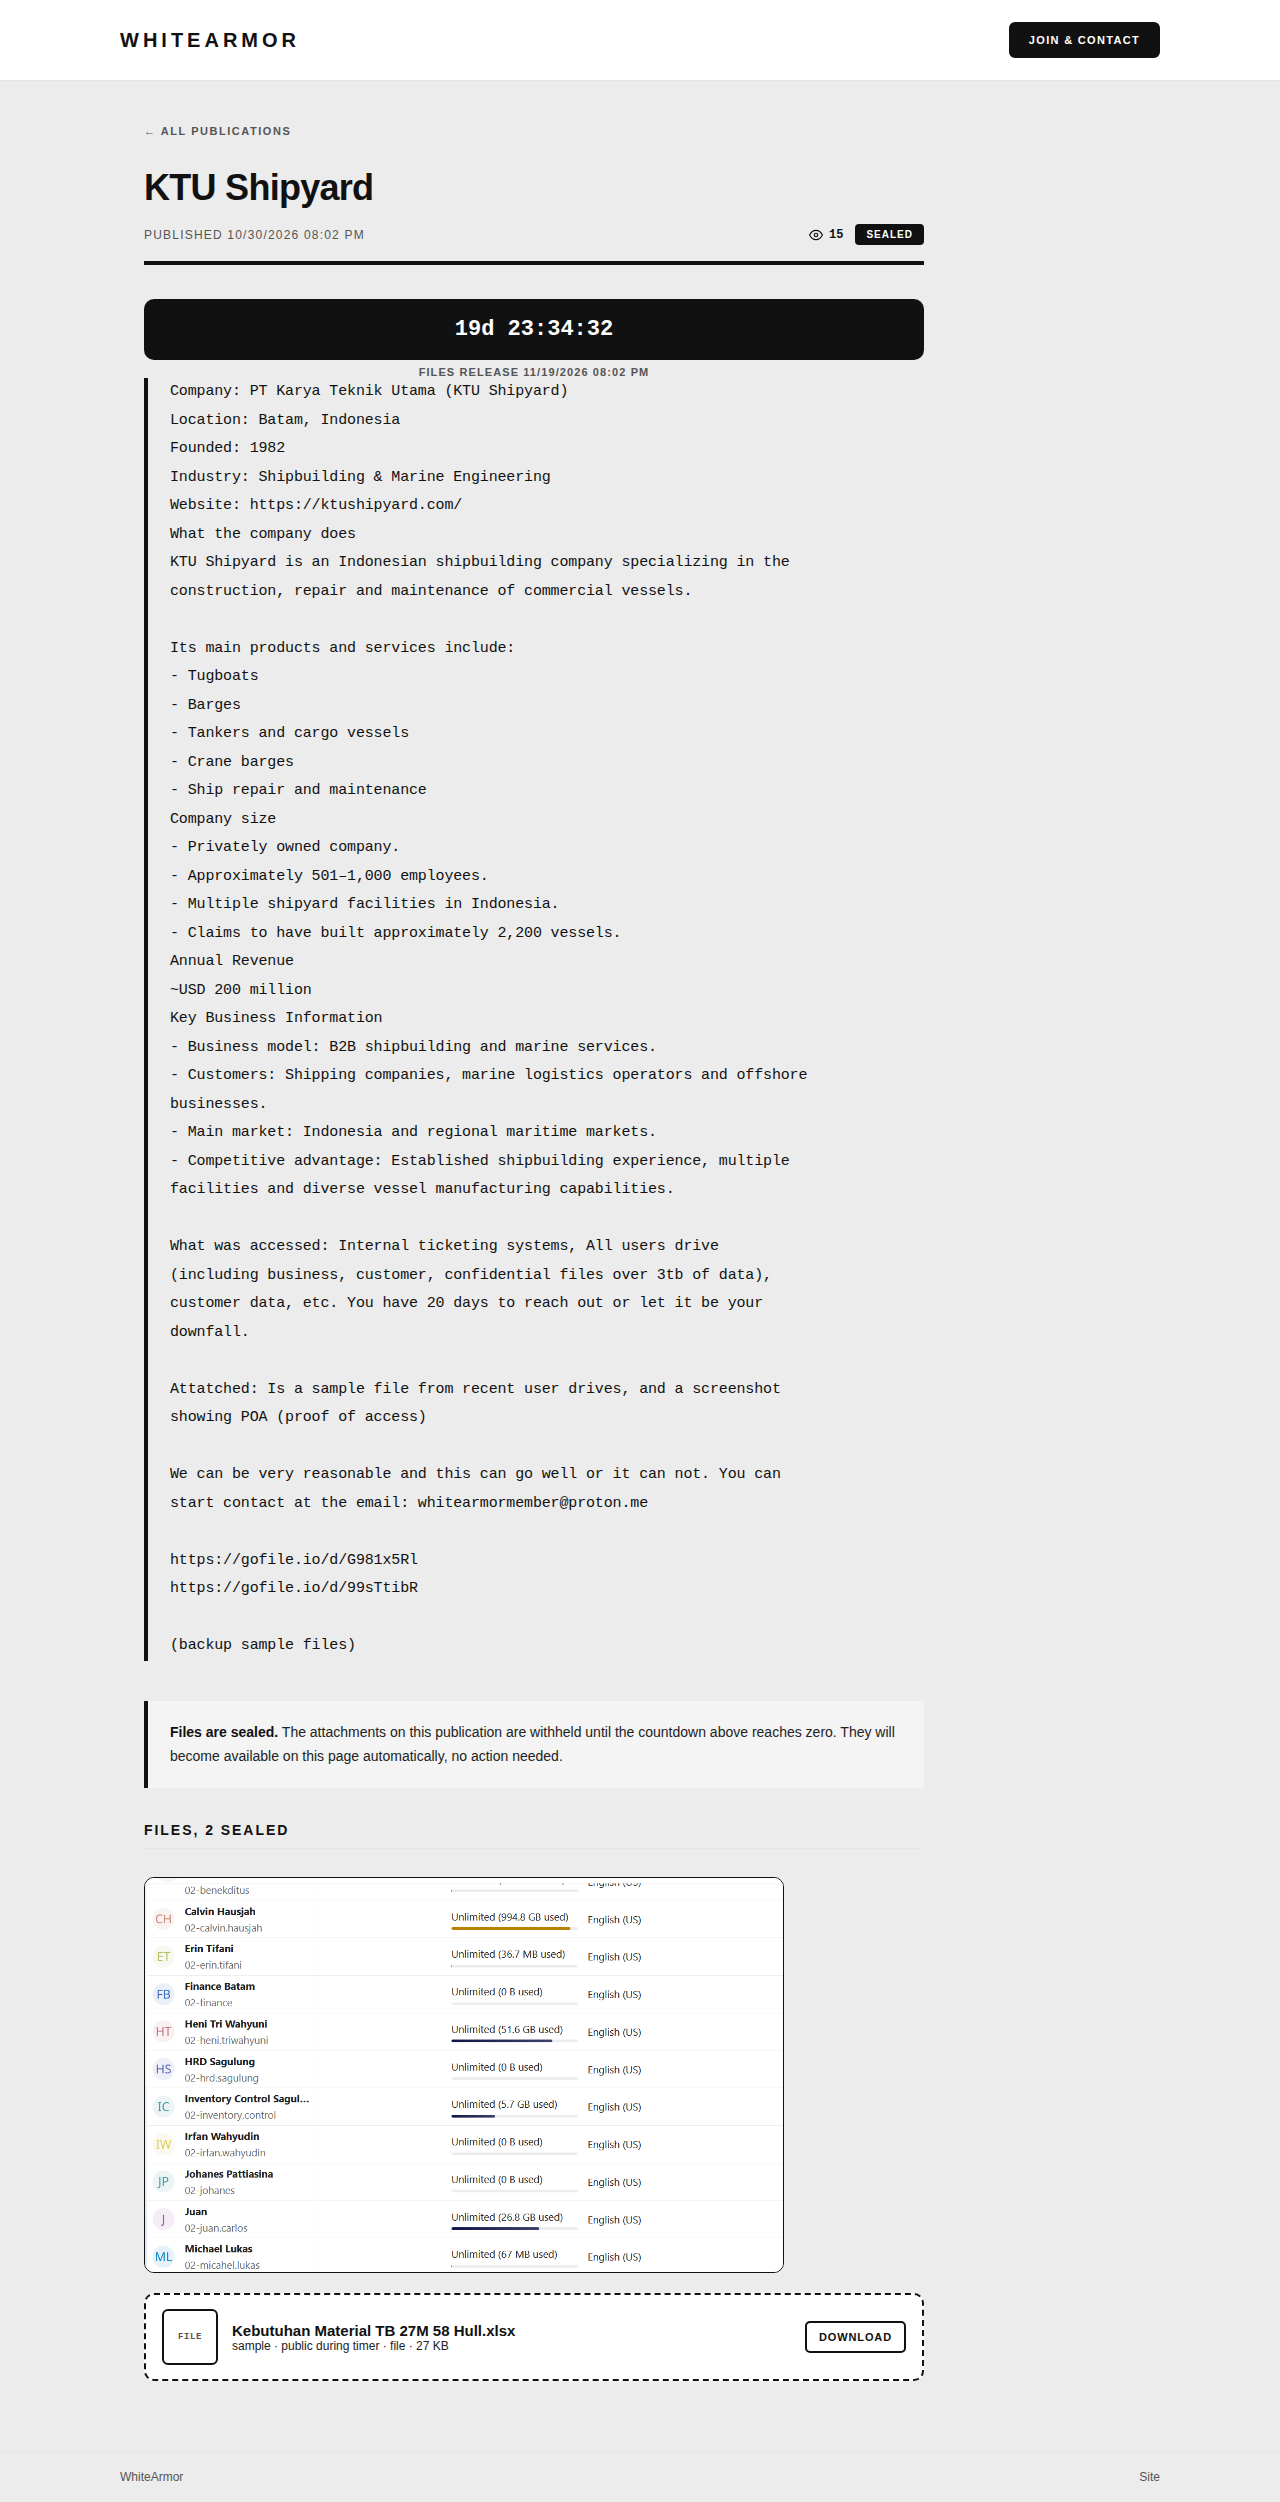
What was accessed: Internal ticketing systems, All users drive (including business, customer, confidential files over 3tb of data), customer data, etc. You have 20 days to reach out or let it be your downfall.
Attatched: Is a sample file from recent user drives, and a screenshot showing POA (proof of access)
We can be very reasonable and this can go well or it can not. You can start contact at the email: whitearmormember@proton.me
https://gofile.io/d/G981x5Rl
https://gofile.io/d/99sTtibR
(backup sample files)
rolly.io
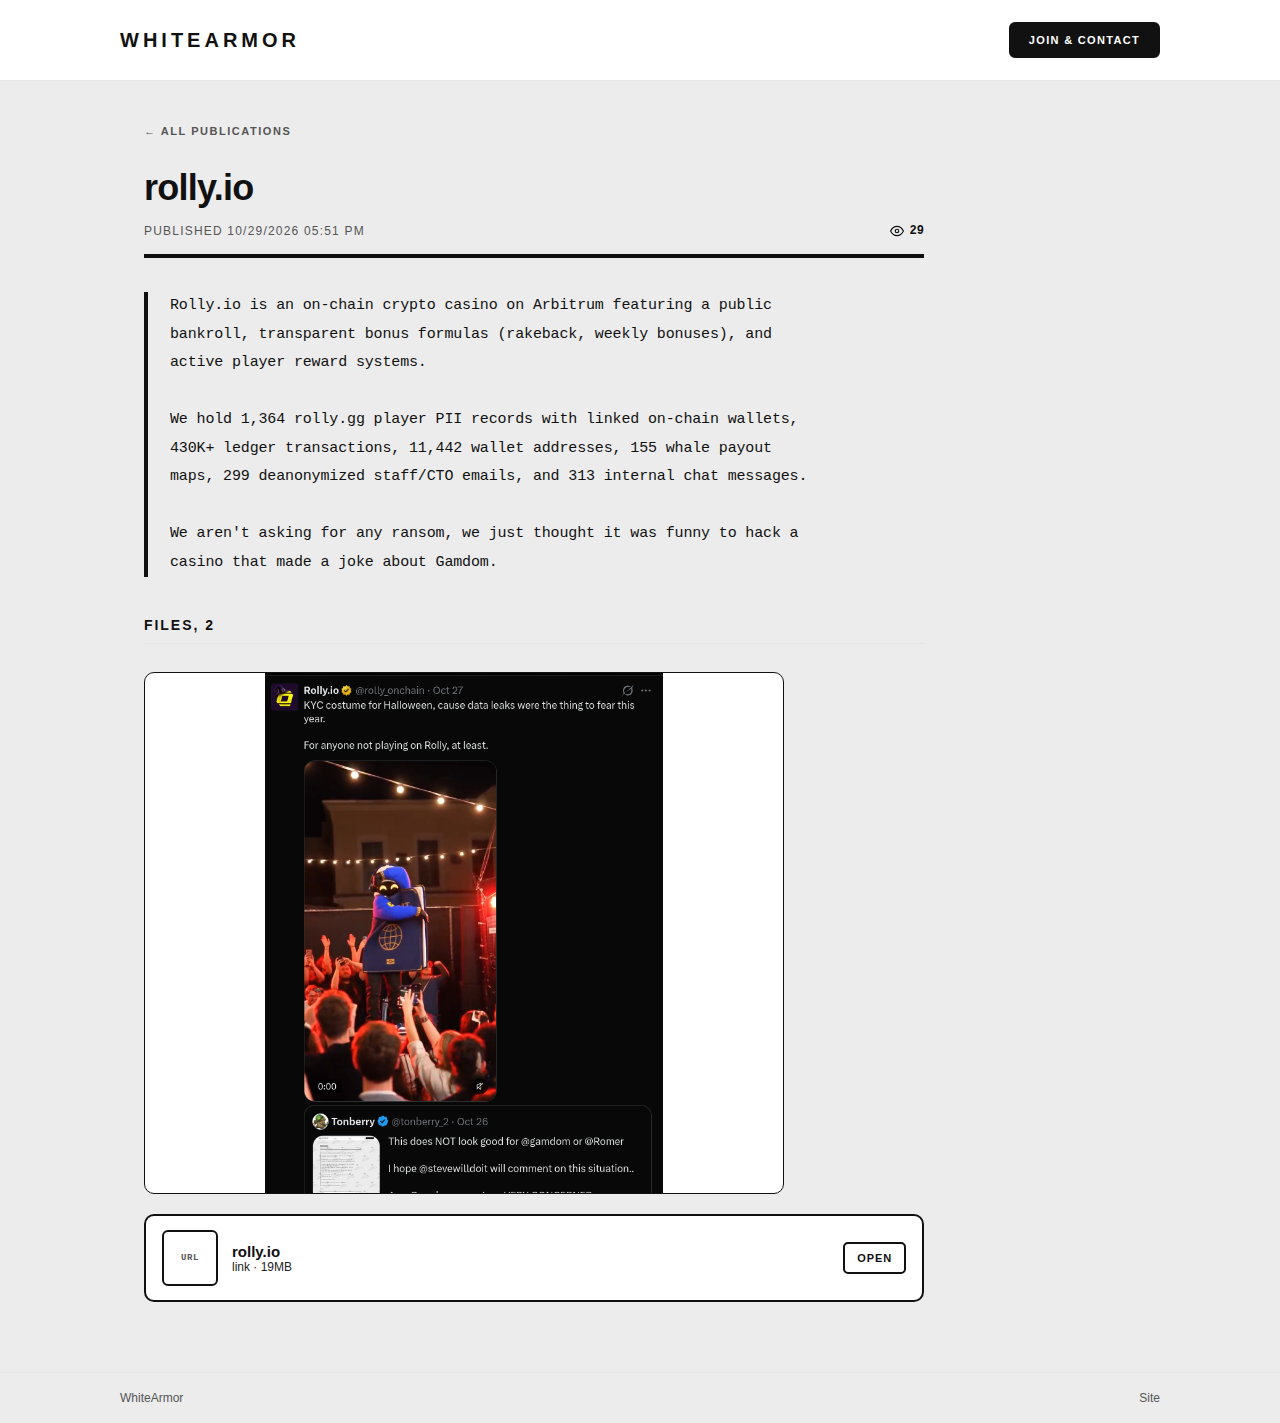
Rolly.io is an on-chain crypto casino on Arbitrum featuring a public bankroll, transparent bonus formulas (rakeback, weekly bonuses), and active player reward systems.
We hold 1,364 rolly.gg player PII records with linked on-chain wallets, 430K+ ledger transactions, 11,442 wallet addresses, 155 whale payout maps, 299 deanonymized staff/CTO emails, and 313 internal chat messages.
We aren't asking for any ransom, we just thought it was funny to hack a casino that made a joke about Gamdom.
Ryder
Ryder is a Fortune 500 transportation and supply chain management company providing fleet management, dedicated transportation, and logistics solutions.
What we hold: 18.75M rows, 328 CSVs, consumer names, phones, emails, driver/associate PII, cleartext API keys, LMS credentials, FTP/telematics configs from RyderView, RLM, EFT.
Our demand is only $20M in BTC... i swear.
Samples can be found below.
Emails with instructions will be sent to Ryder shortly, and no we did not buy access from 'shadowbyte' or whatever the niggas name is on pwnforums.
Contact if you do not receive the instructions:
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
Email: whitearmorrxd@proton.me
wagyu.xyz unfairness
wagyu.xyz runs two rigged systems, both proven by the evidence:
1. Rigged coinflip. The site advertises "48% win chance, 4% house edge" (coinflip-public-claim.txt, coinflip-public-terms.json), but server settings aimed for a 4.00% expected edge and the distribution of outcomes is measurably shifted against players: of 2,852 provably-fair-verified flips, 1,417 fell in the 0-48000 band versus 1,325 above 52000, with only 110 in the dead zone (coinflip-measured-odds.json, result_bins). The provably-fair HMAC checks all pass (coinflip-fairness-verify.py, coinflip-sample-seed-chain.json), which only proves the commits weren't tampered per-round; the win thresholds themselves are crooked. Internal accounting confirms: expectedEdge "4.00", actualEdge "2.92" against a published 2% edge, and a 36.49% player win rate (coinflip-house-stats.json, coinflip-settings.json, coinflip-accepted-orders.json).
2. Hidden fee overcharging. Across 28,840 swap/bridge orders totaling ~$264.9M notional, wagyu advertised $1.73M in fees but actually collected $5.64M, hiding $3.9M or 69.28% of its real take (fee-overcharge-metrics.json). 13,190 orders were charged above the quoted rate, 1,812 above 2 percentage points. The server's internal policy charges up to 10% where the public disclosure says 2% (fee-policy-server.json vs fee-public-disclosure.txt, fee-policy-feeds.json, fee-overcharge-summary.json). Worst cases are itemized in fee-top100-overcharged.csv, e.g. order RMNCMB: $3.17M swap, quoted 0.02, charged 0.08, $190,092 stolen (fee-order-RMNCMB.json).
Evidence to support this can be found below:
Echo.com
Echo Global Logistics is a Chicago-based, technology-enabled third-party logistics provider offering freight brokerage and integrated supply chain services, including truckload, LTL, warehousing, and cross-border shipping across North America.
We hold Echo Global Logistics data: 2.06M claims rows, 153,727 freight loads, 261,440 quotes ($705M buy volume), 136,273 tenderings, 59,607 tracking records, 3,890 employee identity mappings with emails, 2,418 customers, 9,122 carriers, and warehouse geodata.
We suggest you pay a small ransom demand of $10,000,000 in BTC and move on with your lives.
Emails with instructions will be sent to you shortly.
Samples can be found below.
Contact:
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
Email: whitearmorrxd@proton.me
https://t.me/whitearmorxd
Hi, join our telegram channel for fun.. i guess
https://t.me/whitearmorxd
Kucoin
Dear Kucoin,
We are NOT a hacktivist group. We focus mainly on data extortion & ransomware, so please fuck off with your hacktivist bullshit.
https://www.kucoin.com/news/flash/hacktivist-group-whitearmor-claims-to-steal-15-42-million-gamdom-accounts-demands-15m-in-bitcoin
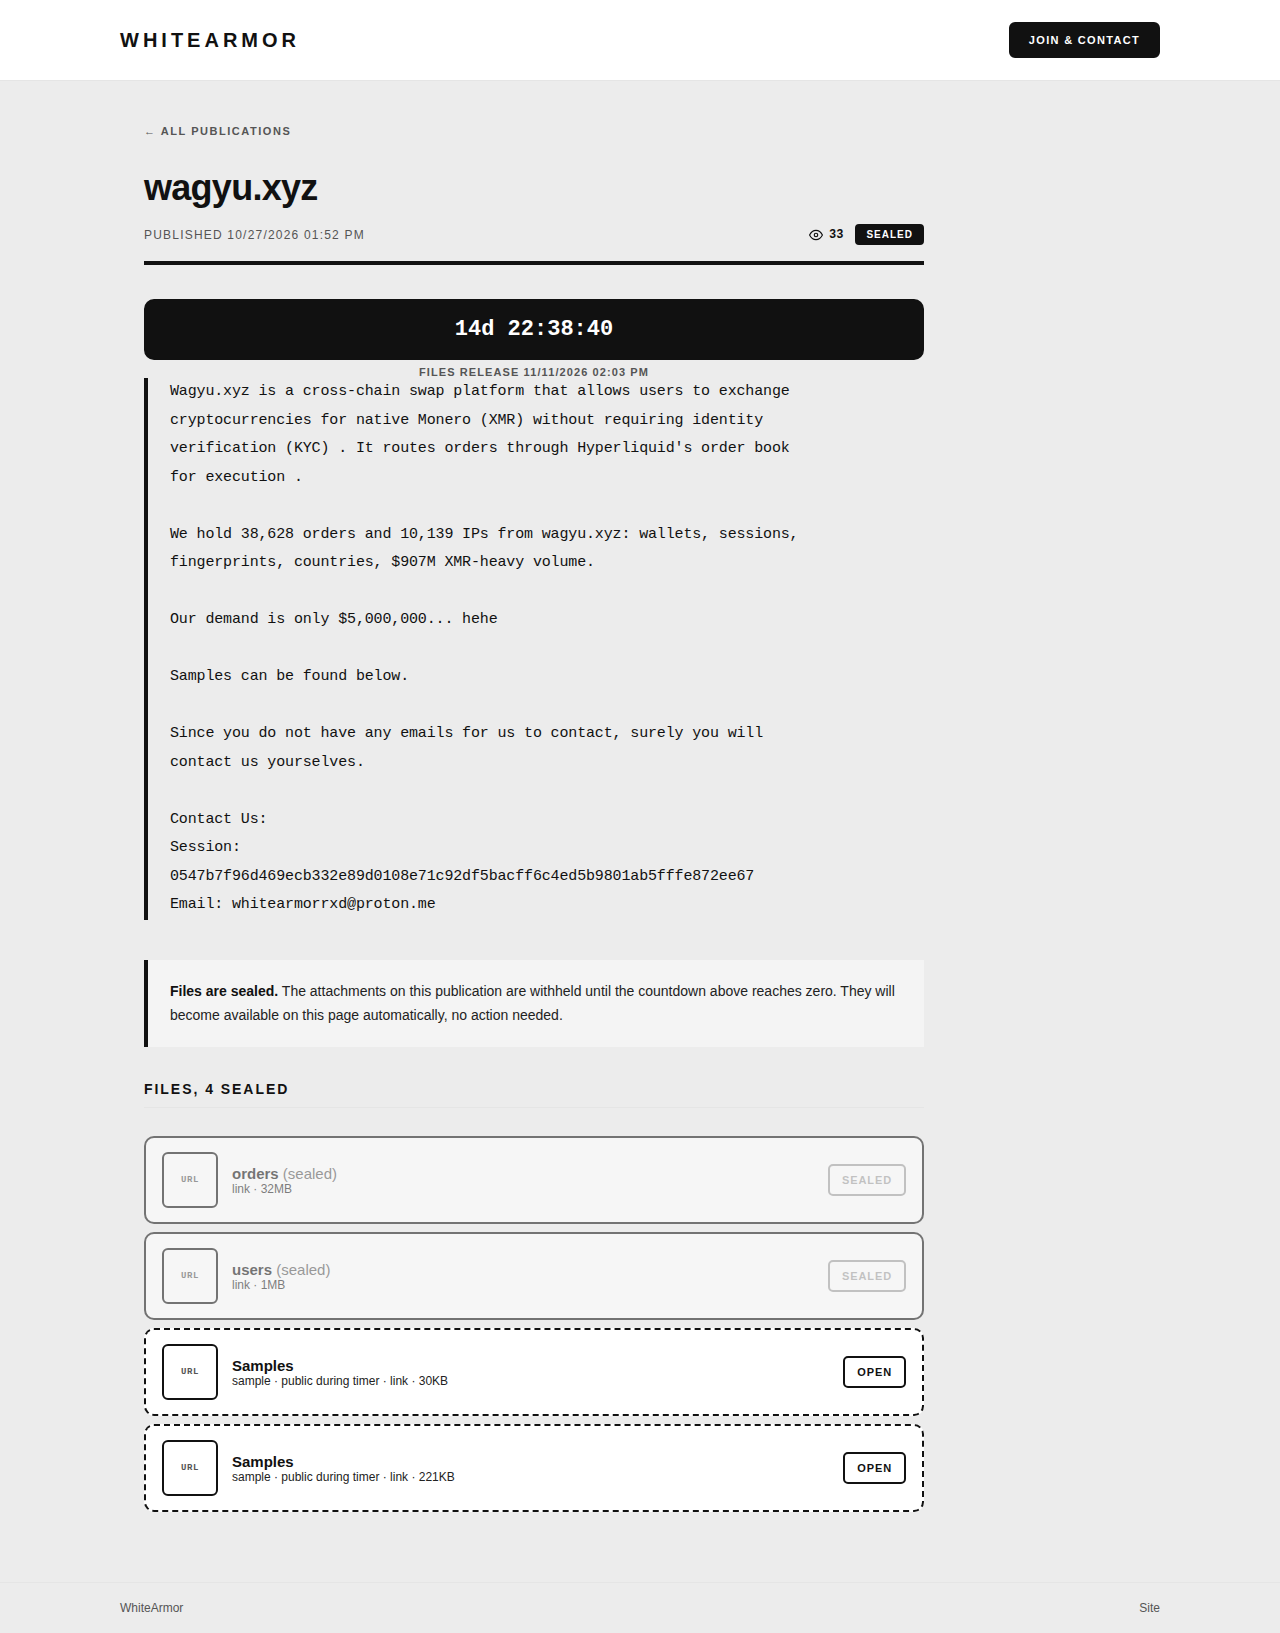
wagyu.xyz
Wagyu.xyz is a cross-chain swap platform that allows users to exchange cryptocurrencies for native Monero (XMR) without requiring identity verification (KYC) . It routes orders through Hyperliquid's order book for execution .
We hold 38,628 orders and 10,139 IPs from wagyu.xyz: wallets, sessions, fingerprints, countries, $907M XMR-heavy volume.
Our demand is only $5,000,000... hehe
Samples can be found below.
Since you do not have any emails for us to contact, surely you will contact us yourselves.
Contact Us:
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
Email: whitearmorrxd@proton.me
gamblinglore
Verification for Gamblinglore.com
Gamdom
Gamdom is an unregulated crypto casino and sportsbook founded in 2016. It recently suffered a hot-wallet breach, with founder Felix Romer reporting over $3 million in losses, though on-chain analysts estimate the damage closer to $4.2 million.
We hold Gamdom's full user database, 15,420,003 accounts with 146 columns, with Gamdom's total combined profit value exceeding $1 billion.
The way in was something internal, a machine account that was already sitting in their admin side (Metawin).
Issued years back, nobody ever rotated it. Never meant to leave the building.
It had admin reach, and everything after that was their own stuff anyway, their control panels and secret stores.
About your provably fair: what it promised and what it delivered were never the same thing.
We demand $15,000,000 in BTC.
Emails with instructions will be sent to you directly.
To verify, a sample can be found below.
LoveSac
LoveSac (LOVE) is a premium furniture retailer operating more than 250 showrooms across the United States, generating approximately $700 million in annual revenue.
We have obtained a database containing 1,113,285 order records spanning nearly seven years of transactions, from December 2019 through October 2026, with a combined recorded transaction value exceeding $1.62 billion.
Each record contains detailed customer and transaction information, including full customer names, complete billing and shipping addresses, telephone numbers, order numbers, order dates, order statuses, and order grand totals.
Our demand: $500,000 in BTC or XMR
To verify, samples can be found below.
WhiteArmor.cc
Hi, our VPS provider has decided to ban our account. Due to this, whitearmor.cc is down and so is most of the data posted on our DLS.
Everything will be back up within a day or two. One tip, do NOT use https://stealthvm.net/ XD
J.B Hunt
You are so stupid JB Hunt. Instead of getting in contact with us & starting the negotiation process, not only did you not announce the breach, you silently email customers demanding them to update their passwords..
Fuck you... ;/
https://x.com/WhiteArmorxd
Hi, we now have an X account.
https://x.com/WhiteArmorxd
Also, fuck the AI slop cti reporters lol
Partido Liberal
Brazil's Liberal Party (PL) is the political party of the Bolsonaro family. Although named "Liberal," it is currently characterized by conservatism and right-wing populism. Jair Bolsonaro joined the party in 2021, and his son Flávio Bolsonaro is now the party's presidential candidate, advocating reduced government intervention and tough security policies.
We hold the complete Partido Liberal (PL, Brazil) dump: 79K member records with CPF/voter ID/RG photos, 374 live cleartext e-Título credentials, 475 operator accounts with shared password, 2.7M audit events, party dossiers (artist payments, deepfakes, ghost donations), vendor PII, and 340K+ member images.
If you don't want this getting out, we suggest you contact us & pay the ransom amount of $5,000,000 in BTC :)
Contact:
Email: whitearmorrxd@proton.me
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
Hisense
Hisense is a Chinese multinational electronics and appliance manufacturer, founded in 1969, known globally for televisions and home appliances.
We hold Hisense's entire GCRM production document store, the full warranty-claims archive for Malaysia/Singapore: customer names, phones, emails, ID numbers, 2,549 suppliers, hundreds of invoices, payments, contracts, RMA forms, claim evidence, plus their internal CRM app binary.
Our demand is $500,000 in BTC. Good luck.
Contact: whitearmorrxd@proton.me
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
whitearmor.cc
Hi!
We now have a clearnet domain for easy-access.
WhiteArmor.cc
JB Hunt
J.B. Hunt is a major North American transportation and logistics company providing intermodal, dedicated, and truckload services via its digital freight marketplace.
We hold 140,838 employee records with PII and national IDs, 1.7M carrier contacts, 38.2M invoices, 187K RBAC permission records, 3,196 ranked account-takeover targets, 973 M365 mailboxes, 374K organizations.
Our demand: $5,000,000, in BTC or XMR. Instructions to follow by email.
To verify, samples can be found below.
Contact:
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
Email: whitearmorrxd@proton.me
Whirlpool
Whirlpool is a global home appliance manufacturer (NYSE: WHR) making washers, fridges, and cooking appliances under brands like KitchenAid and Maytag. Its 2025 annual revenue was about $15.52 billion.
We hold 4,577 Whirlpool employee records across three plants, names, AD-style usernames, managers, cost centers, shifts, along with 374 corporate emails, ~22,000 SAP invoice records, and the full plant contact infrastructure. Pay, and this stays quiet. Don't, and the data goes public.
We want $140,000 in BTC or XMR. You will receive an email containing instructions on how to proceed.
Samples:
https://biteblob.com/Information/mNTP6w0lBW8P9l/#samples.zip
Contact:
whitearmorrxd@proton.me
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
W.A
Hello,
We are WhiteArmor, an organization focused on data-theft extortion, with further motive to expand in to ransomware operations when considered big enough.
We are currently seeking the following people of roles and experiences:
Penetration testers
Web-exploitation
Zero-day research
A word due; if you are unfamiliar with the experiences slash roles listed above, do not consider attempting to join. Should you attempt to contact us and join, you will be blocked.
Our fee if you hit a successful ransom payout is 5%. The rest is yours.
Our contacts are available on our DLS below;
http://whitearz6uvtfdefgsc4r3mzmyswtte65k5umcmv6cu6zhi4l5k4irad.onion/
Updates.
Hi all; spots within the group are still open. If you're looking to join, you can find our contact information at the top right. Our ransomware is nearly complete, and we have multiple companies lined up to list, including Fortune 500 companies and multi-billion-dollar revenue firms.
To be clear, we're not just some random skid group. We are releasing Disney's Staff Directory as a little start to our group, though more to come. Anyways, enjoy.
This data is unrelated to the NullBulge leak; it was exfiltrated via a JWT authentication bypass vulnerability in the gateway.