Hi, we now have an X account.
https://x.com/WhiteArmorxd
Also, fuck the AI slop cti reporters lol
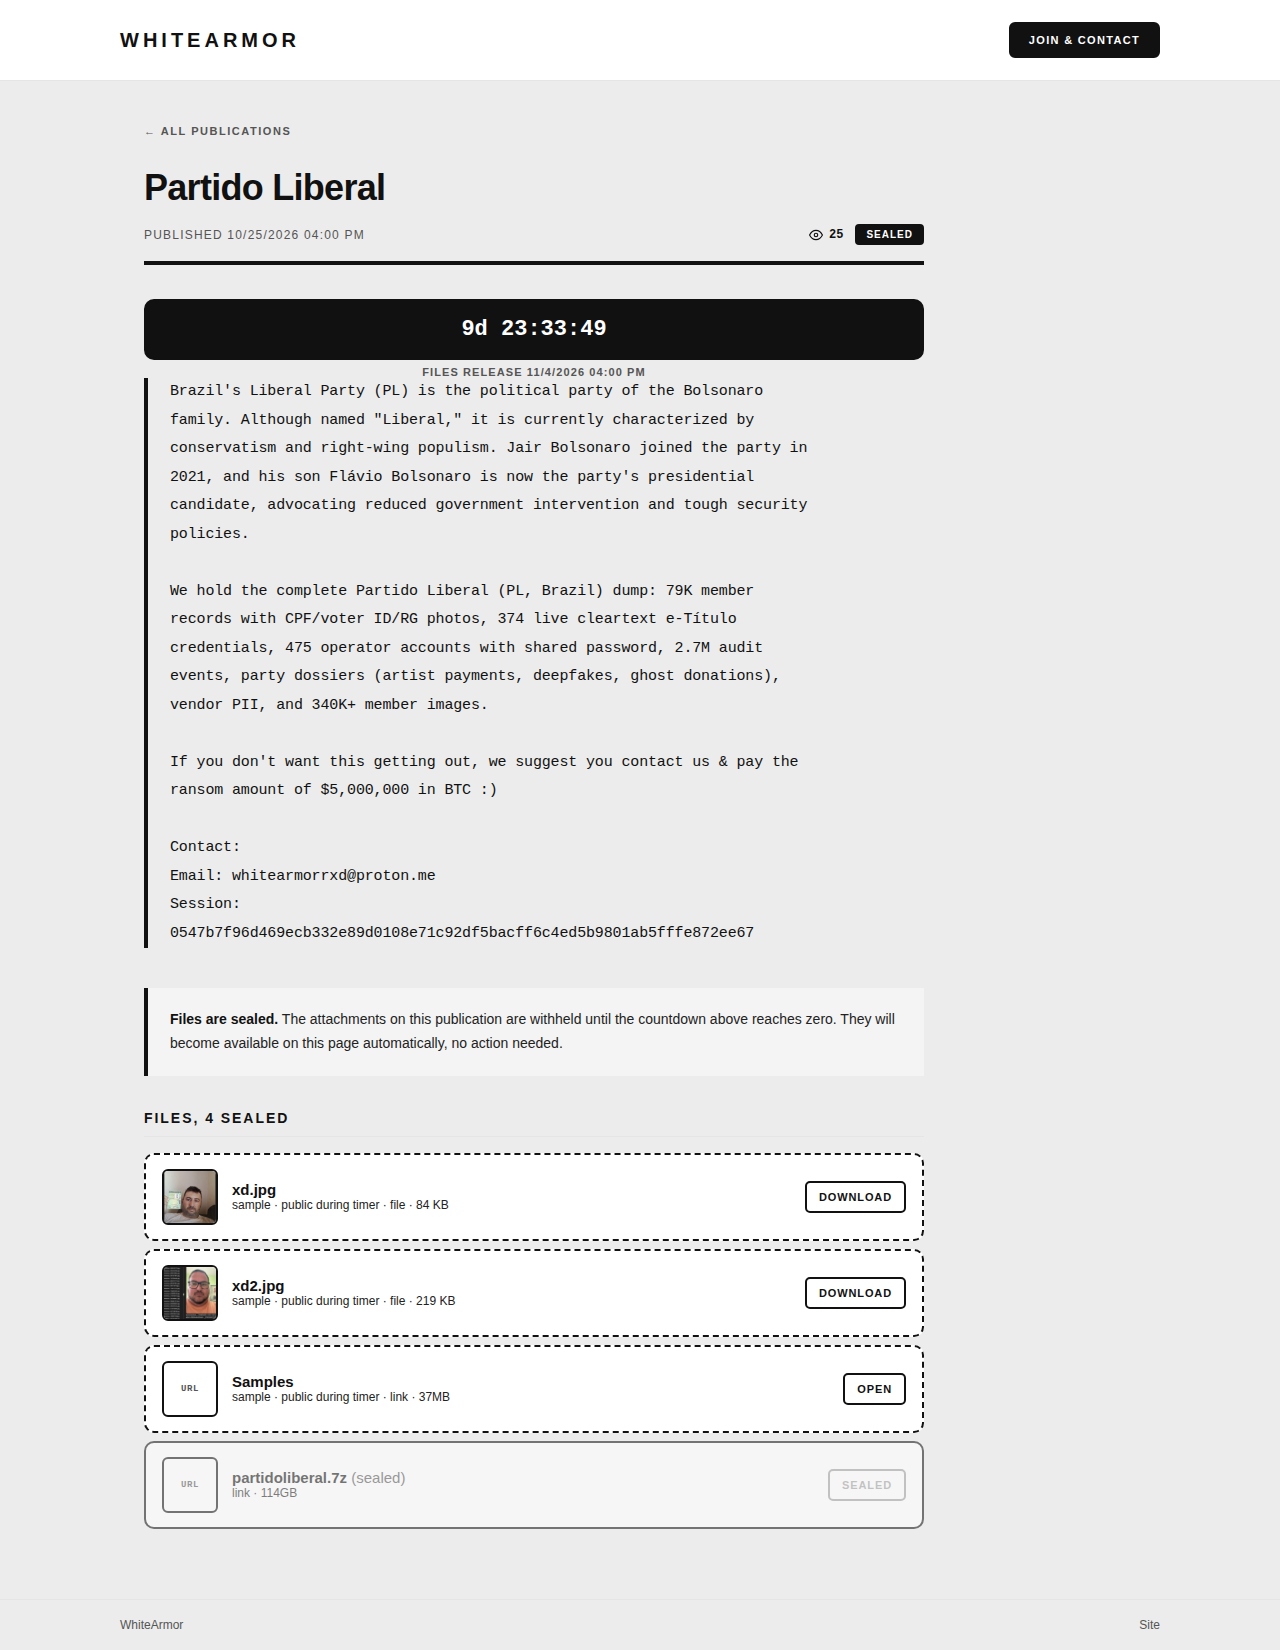
Partido Liberal
Brazil's Liberal Party (PL) is the political party of the Bolsonaro family. Although named "Liberal," it is currently characterized by conservatism and right-wing populism. Jair Bolsonaro joined the party in 2021, and his son Flávio Bolsonaro is now the party's presidential candidate, advocating reduced government intervention and tough security policies.
We hold the complete Partido Liberal (PL, Brazil) dump: 79K member records with CPF/voter ID/RG photos, 374 live cleartext e-Título credentials, 475 operator accounts with shared password, 2.7M audit events, party dossiers (artist payments, deepfakes, ghost donations), vendor PII, and 340K+ member images.
If you don't want this getting out, we suggest you contact us & pay the ransom amount of $5,000,000 in BTC :)
Contact:
Email: whitearmorrxd@proton.me
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
Hisense
Hisense is a Chinese multinational electronics and appliance manufacturer, founded in 1969, known globally for televisions and home appliances.
We hold Hisense's entire GCRM production document store, the full warranty-claims archive for Malaysia/Singapore: customer names, phones, emails, ID numbers, 2,549 suppliers, hundreds of invoices, payments, contracts, RMA forms, claim evidence, plus their internal CRM app binary.
Our demand is $500,000 in BTC. Good luck.
Contact: whitearmorrxd@proton.me
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
whitearmor.cc
Hi!
We now have a clearnet domain for easy-access.
WhiteArmor.cc
JB Hunt
J.B. Hunt is a major North American transportation and logistics company providing intermodal, dedicated, and truckload services via its digital freight marketplace.
We hold 140,838 employee records with PII and national IDs, 1.7M carrier contacts, 38.2M invoices, 187K RBAC permission records, 3,196 ranked account-takeover targets, 973 M365 mailboxes, 374K organizations.
Our demand: $5,000,000, in BTC or XMR. Instructions to follow by email.
To verify, samples can be found below.
Contact:
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
Email: whitearmorrxd@proton.me
Whirlpool
Whirlpool is a global home appliance manufacturer (NYSE: WHR) making washers, fridges, and cooking appliances under brands like KitchenAid and Maytag. Its 2025 annual revenue was about $15.52 billion.
We hold 4,577 Whirlpool employee records across three plants, names, AD-style usernames, managers, cost centers, shifts, along with 374 corporate emails, ~22,000 SAP invoice records, and the full plant contact infrastructure. Pay, and this stays quiet. Don't, and the data goes public.
We want $140,000 in BTC or XMR. You will receive an email containing instructions on how to proceed.
Samples:
https://biteblob.com/Information/mNTP6w0lBW8P9l/#samples.zip
Contact:
whitearmorrxd@proton.me
Session: 0547b7f96d469ecb332e89d0108e71c92df5bacff6c4ed5b9801ab5fffe872ee67
W.A
Hello,
We are WhiteArmor, an organization focused on data-theft extortion, with further motive to expand in to ransomware operations when considered big enough.
We are currently seeking the following people of roles and experiences:
Penetration testers
Web-exploitation
Zero-day research
A word due; if you are unfamiliar with the experiences slash roles listed above, do not consider attempting to join. Should you attempt to contact us and join, you will be blocked.
Our fee if you hit a successful ransom payout is 5%. The rest is yours.
Our contacts are available on our DLS below;
http://whitearz6uvtfdefgsc4r3mzmyswtte65k5umcmv6cu6zhi4l5k4irad.onion/
Updates.
Hi all; spots within the group are still open. If you're looking to join, you can find our contact information at the top right. Our ransomware is nearly complete, and we have multiple companies lined up to list, including Fortune 500 companies and multi-billion-dollar revenue firms.
To be clear, we're not just some random skid group. We are releasing Disney's Staff Directory as a little start to our group, though more to come. Anyways, enjoy.
This data is unrelated to the NullBulge leak; it was exfiltrated via a JWT authentication bypass vulnerability in the gateway.